London · 15 September 2027 · JW Marriott Grosvenor House

Agenda & Speakers

The programme

The UK's biggest dedicated AI security and data protection agenda.

Short, sharp and interactive: keynotes and case studies from practitioners, live panels you vote in, peer roundtables on the problems you name, and two hours of structured networking by design.
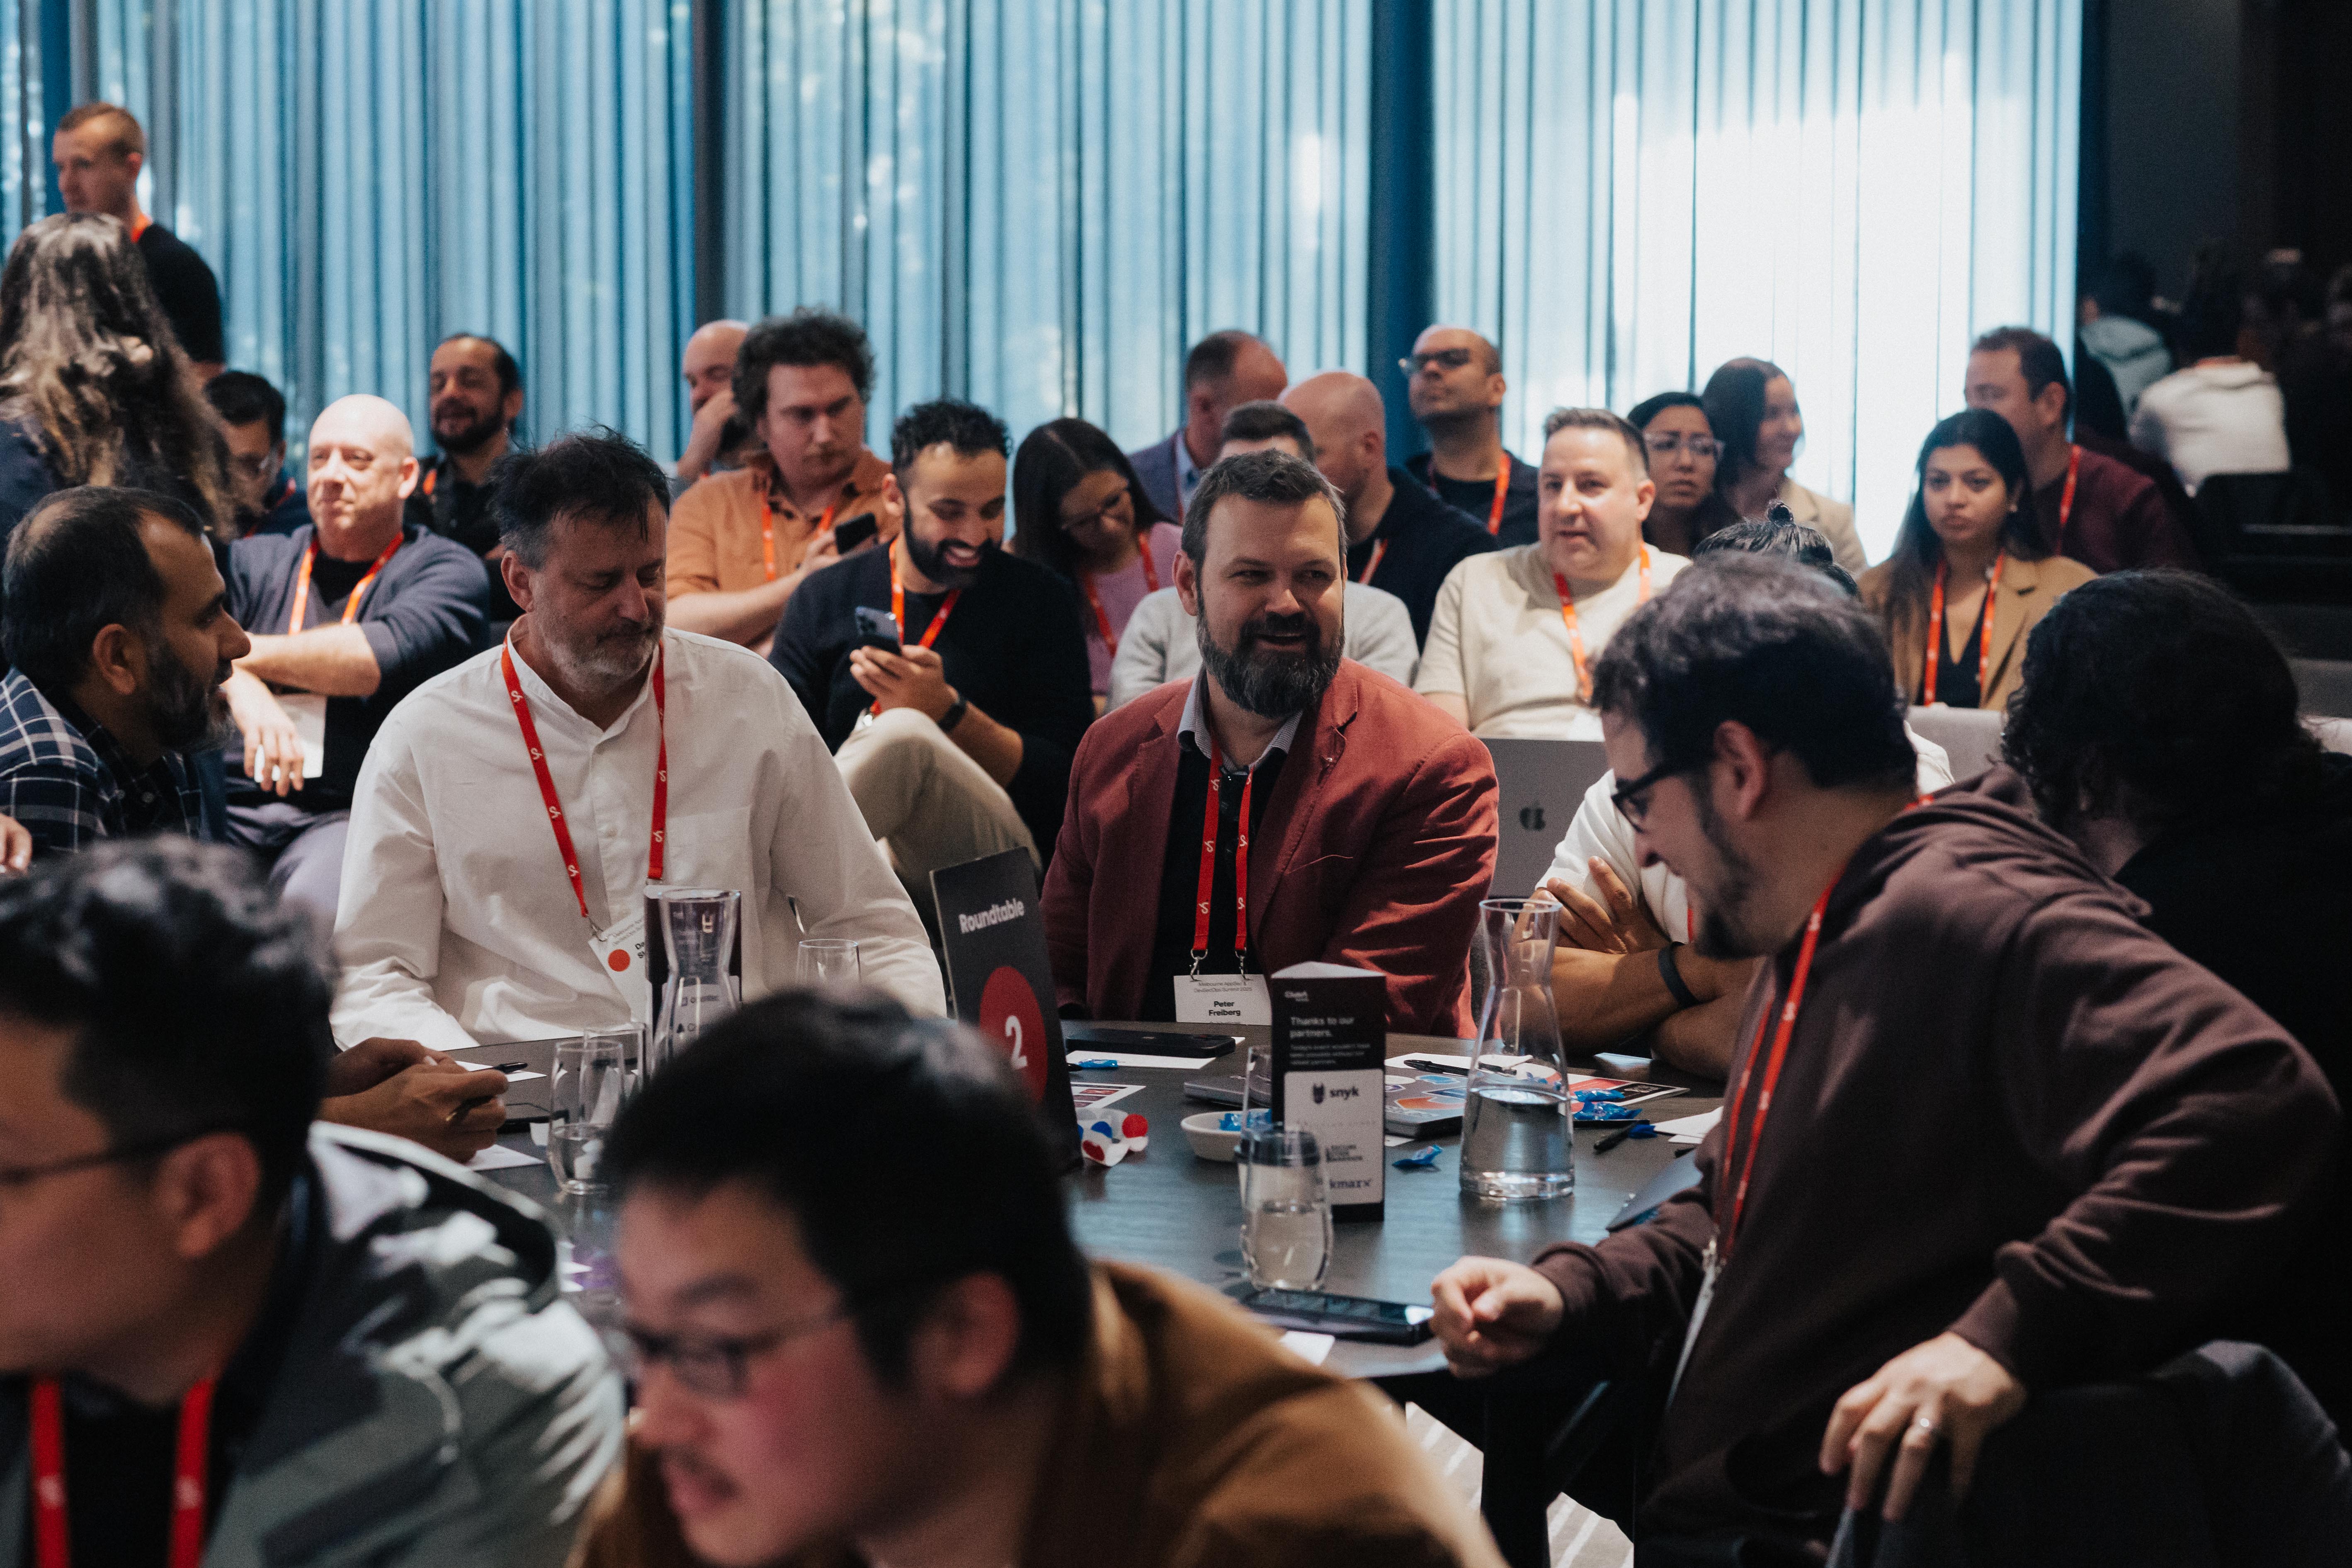
AI + Data Security World London
Confirmed for 2027

Meet the 2027 speakers.

Speakers are announced on a rolling basis. Sign up for updates to hear each announcement first.

Speaker lineup will be released in 2027.
Agenda

Wednesday 15 September 2027.

All times BST. Sessions are announced and updated on a rolling basis.

08:30

Registration Opens & Networking Breakfast

Networking
Plenary
+

Beat the rush and join us early for complimentary barista-made coffee and breakfast.

09:15

Welcome & Opening Remarks

Plenary
+
09:20

Keynote: Building Secure, Trustworthy, and Resilient AI Systems

Keynote
AI Security & Governance
+

Generative and agentic AI have moved from experimentation to production faster than most security and governance functions can keep pace with, and the organisations getting this right are treating security and trust as design requirements, not afterthoughts bolted on post-launch. This opening keynote frames the day: what "trustworthy AI" actually requires in practice, and the shape of the threats and expectations now converging on organisations running AI at scale.

  • Why AI trust and resilience are now board-level priorities, not just a technical concern
  • The forces reshaping AI risk right now: attackers, regulators, shadow adoption, and agentic autonomy
  • What secure-by-design actually looks like for production AI systems
09:40

Keynote: Redesigning Access Controls for an AI-Augmented Workforce

Keynote
Data Protection & Security
+

As AI copilots, agents, and analytics tools require broader, faster access to enterprise data to deliver value, organisations face a widening tension between empowering AI-augmented employees and maintaining the access discipline that data protection has always depended on.

  • How AI agents and copilots blur the traditional boundary between "user" and "system," and why identity and access management frameworks built for people don't cleanly extend to autonomous tools.
  • Moving away from broad, standing permissions toward dynamic, context-aware access that grants AI tools and employees only what's needed for the task at hand.
  • Giving finance and business leaders a practical framework for weighing productivity gains from broader data access against quantifiable increases in breach exposure and regulatory risk.
10:10

Panel Discussion: How Cybercriminals Are Using AI to Accelerate Attacks

Panel
AI Security & Governance
+

Threat actors have moved from experimenting with AI to industrialising it, using it to scale phishing, write malware, and compress attack timelines from weeks to hours. This panel brings together practitioners tracking this shift to unpack what's actually changed in attacker tradecraft, and what defenders need to do differently as a result.

  • How AI has compressed attacker dwell time and reconnaissance-to-breach timelines
  • Real examples of AI-generated malware, phishing, and social engineering at scale
  • Where defensive AI can realistically keep pace with offensive AI, and where it can't
10:40

How I Solved… Shutting Down Shadow AI Without Shutting Down Innovation

Case study
Data Protection & Security
+

With employees adopting AI tools faster than IT could track or approve them, one security leader built a discovery and governance approach that brought unauthorised AI usage into the light — without triggering a workforce backlash or slowing legitimate innovation.

  • How the team mapped unsanctioned AI tool usage across the organisation before deciding on any policy response, since you can't govern what you can't see.
  • Designing an approval pathway fast enough that employees chose to use it rather than route around it, turning shadow AI into managed AI.
  • Building lightweight, continuous visibility into new AI tools.
10:55

Morning Tea & Networking

Break
Plenary
+
11:25

Audience Activity

Workshop
AI Security & Governance
+

A hands-on, interactive session working through a real AI security and governance scenario as a room. Details announced soon.

11:40

How I Solved… Securing Legacy Systems That Can't Be Replaced Overnight

Case study
Data Protection & Security
+

With critical infrastructure and legacy platforms too costly or risky to replace outright, one security leader built a layered protection strategy that meaningfully reduced risk exposure without waiting for a full modernisation program.

  • Triaging legacy system vulnerabilities realistically, rather than pursuing an unachievable "patch everything" strategy.
  • How network segmentation, enhanced monitoring, and strict access controls around legacy systems provided durable risk reduction, not just a stopgap.
  • Building the business case for ongoing investment in legacy security, when the instinct is often to deprioritise spending on systems slated for eventual retirement.
11:55

How I Solved… Prompt Injection and AI Agent Security

Case study
AI Security & Governance
+

Prompt injection remains the leading cause of agentic AI security failures in production, and as agents gain the ability to act, not just respond, the blast radius of a successful injection grows sharply. This case study walks through a real prompt injection incident against an agentic system, what it exposed about the architecture, and the guardrails built afterward.

  • Anatomy of a real prompt injection attack against a production AI agent
  • Why prompt injection is proving structurally difficult to fully patch, not just fix once
  • The guardrails, sandboxing, and human-in-the-loop checkpoints added after the incident
12:10

Panel: Legal Liability and Trust in an AI-Driven Data Landscape

Panel
Data Protection & Security
+

As AI systems make decisions with real legal and financial consequences, organisations are discovering that liability frameworks built for human decision-making don't map cleanly onto AI-driven processes; leaving legal, privacy, and security leaders to navigate accountability, contracts, and customer trust largely without settled precedent.

  • When an AI system's decision leads to a data breach, discriminatory outcome, or regulatory breach, how are legal teams currently allocating fault between the organisation, the AI vendor, and the underlying model provider; and where does existing law simply not have an answer yet?
  • How eroded customer trust following an AI-related incident is increasingly translating into legal action and what that means for how legal and privacy teams collaborate on incident response.
  • Exploring the tension between regulatory and legal expectations for transparency and explainability, and the practical reality that many AI systems can't yet provide a clear, defensible account of how a specific decision was made.
12:40

Peer Roundtables

Workshop
AI Security & Governance
+

Small-group, discussion-based sessions where you'll work through real AI security and governance challenges with peers in similar roles. Roundtable topics will be announced soon.

13:30

Lunch & Networking

Break
Plenary
+
14:20

QuickFire Quiz: Test Your Knowledge Against Your Peers

Networking
Plenary
+

Put your knowledge to the test in this fast-paced quiz covering real-world trivia, key concepts, and emerging trends. Compete for bragging rights — and a voucher — as the top scorer takes the crown.

14:35

How I Solved… Cutting Breach Detection Time from Weeks to Hours

Case study
Data Protection & Security
+

Facing a security team stretched thin and alert fatigue eroding response quality, one CISO restructured detection and triage around automation and prioritisation; dramatically compressing the time between compromise and containment.

  • How the team re-engineered alert prioritisation so analysts spent time on genuine threats instead of drowning in low-value notifications.
  • Where automated containment actions (isolating endpoints, revoking access) were safely delegated to systems versus kept as human decisions.
  • How the leader secured budget and buy-in for detection tooling improvements proactively, before an incident forced the issue.
14:50

Keynote: Board Accountability and AI Risk Reporting

Keynote
AI Security & Governance
+

Boards are being asked to oversee AI risk without always having the technical grounding to interrogate it properly, and regulators are starting to expect documented accountability, not just good intentions. This closing keynote translates AI security and governance risk into the language and cadence boards actually need.

  • What a genuinely useful AI risk report looks like at board level
  • Where accountability for AI risk should sit, and why "everyone" usually means no one
  • Building board AI literacy without turning every meeting into a technical briefing
15:10

Think Tank: Third-Party and Supply Chain Risk: Securing Data You Don't Fully Control

Panel
Data Protection & Security
+

As enterprises rely on growing networks of AI vendors, SaaS platforms, and outsourced service providers, sensitive data increasingly flows through systems organisations neither built nor fully control; turning vendor risk management into one of the hardest unsolved problems in data protection.

  • Why static vendor assessments fail to capture real-time risk, and what continuous monitoring of third-party access actually looks like in practice.
  • The unique challenges of assessing AI and model providers, where questions about training data use, data retention, and model behaviour go beyond traditional security due diligence.
  • Lessons from real incidents on managing incident response, regulatory notification, and reputational fallout when the failure originated outside your own walls.
15:40

Closing Remarks & Prize Draw

Plenary
+
15:45

Networking Drinks Hour

Networking
Plenary
+

Unwind with your peers for a couple of drinks on us!

16:45

Event Closed

Plenary
+
Past speakers

Who has taken the stage before.

Leaders who have shared their work at previous AI + Data Security World events.

Angela Dunbar
Angela Dunbar
Head of Privacy, Information and Knowledge Management
Corey M. Dennis
Corey M. Dennis
Assistant General Counsel & Chief Privacy Officer
Doug Hammond
Doug Hammond
Chief Information Security Officer
Eliza Knapp
Eliza Knapp
Director of Privacy - Data and AI
Kate Carruthers
Kate Carruthers
Lecturer
Lisa McCallum
Lisa McCallum
Chief Data Officer, Cancer Institute NSW
Manoj S
Manoj S
Director - AI/ML, Cloud Platform, Data, Security Architecture & Engineering
Maya Goethals
Maya Goethals
Director, Compliance & Operational Risk
Sherief Ahmed
Sherief Ahmed
Chief Privacy Officer and IT Director Internal Audit and Analytics
Vasant Prabhu
Vasant Prabhu
Global Data Protection Lead (AI, Privacy & Cybersecurity Architecture)
Wayne Clarke
Wayne Clarke
Deputy General Counsel – Privacy, Data, AI & Cyber
Willie Session
Willie Session
Chief Information Security Officer
Wednesday 15 September 2027 · JW Marriott Grosvenor House

Don't miss the UK's biggest AI security and data protection event.

Insights

Go deeper

AI security & governance
Shadow AI Governance: How to Find It, Govern It and Stop the Data Leaking

Shadow AI is unsanctioned AI use inside your company. Learn how to discover it, write a policy people follow, and stop sensitive data leaking into LLMs.

October 2, 2026
Data protection & governance
DSPM for the AI Era: What Data Security Posture Management Has to Do Before You Switch On Copilot, RAG or Agents

DSPM (data security posture management) for buyers: what it must do before Copilot, RAG and agents touch your data, and how it differs from CSPM and DLP.

October 2, 2026
AI security & governance
AI TRiSM Explained: The Four Pillars, Who Owns Them, and How to Stand Up a Program

AI TRiSM explained for CISOs and data leaders: the four pillars, who owns each, and how to map the program to NIST AI RMF and ISO 42001.

October 2, 2026
All insights